Understanding AI-driven cyberattacks and how to defend against them is the ultimate operational imperative for modern security teams and enterprise leaders. Cybercriminals have abandoned manual script execution in favor of autonomous threat agents, generative social engineering, and real-time deepfakes. These tools compress the attack lifecycle from days to minutes, systematically exploiting legacy security blind spots. Traditional perimeter controls can no longer stem the tide; defending your network requires behavioral telemetry, phishing-resistant identity architectures, and strict administrative verification protocols.
The Modern AI Threat Landscape
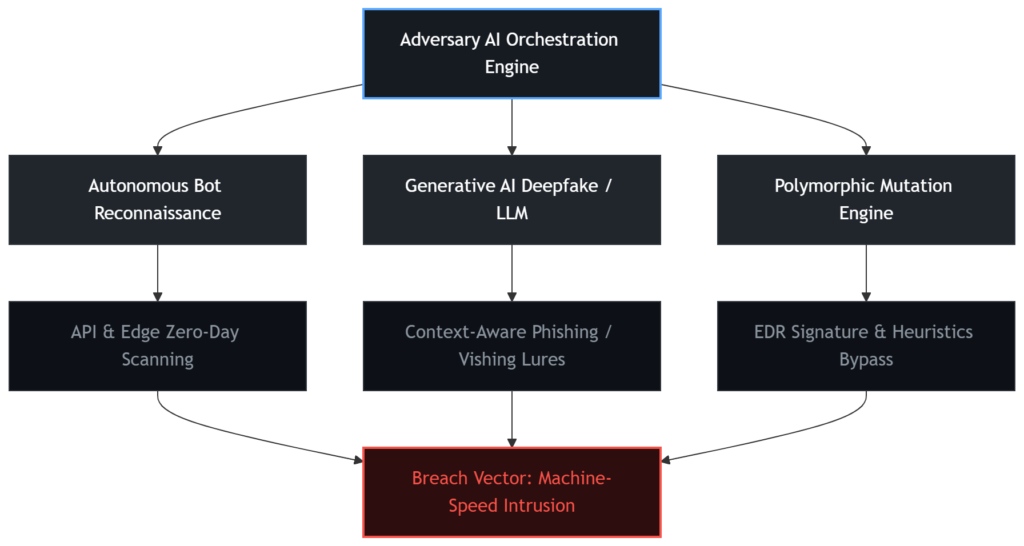
The emergence of accessible artificial intelligence has transformed cybercrime from an industry of manual execution into one of automated, hyper-scalable orchestration. Adversaries leverage specialized Large Language Models (LLMs) and neural networks to execute machine-speed intrusions that easily bypass human observation and static defenses. To benchmark your defense posture against official framework standards, consult the NIST AI Risk Management Framework.
1. Autonomous Reconnaissance Bots
Adversaries deploy autonomous scanning agents programmed to constantly evaluate external attack surfaces. These bots do not merely ping IP ranges; they actively map cloud infrastructure, analyze public API documentation, test edge devices for unpatched zero-days, and map out Active Directory configurations. By executing thousands of probing actions per second, these agents identify micro-misconfigurations within minutes of a deployment going live.
2. LLM-Crafted Social Engineering
Generic phishing emails containing obvious grammatical errors have been replaced by context-aware, zero-defect communications generated by LLMs. By ingesting public data from LinkedIn, corporate press releases, SEC filings, and compromised internal email threads, generative tools construct hyper-personalized spear-phishing lures at scale. The language, tone, and specific internal references make these emails virtually indistinguishable from legitimate corporate communication.
3. Generative Deepfake Vishing
Audio and video cloning technologies now require as little as three seconds of sampled voice data to synthesize high-fidelity, real-time speech. Threat actors execute business email compromise (BEC) attacks by impersonating Chief Executive Officers, Chief Financial Officers, or trusted vendors over phone calls or video web conferences. These deepfakes bypass standard security layers by directly exploiting human trust to authorize fraudulent wire transfers or emergency credential resets.
4. Polymorphic Code Mutation
Static payloads are obsolete. AI-driven malware engines alter their underlying binary structure, encryption keys, and variable names dynamically prior to each execution. By continually changing their code signatures while maintaining core malicious functionality, polymorphic variants render traditional hash-based detection engines and static heuristic rules completely ineffective.
Why Legacy Security Stacks Fail?
Modern enterprise security stacks were built on the assumption that threat actors exhibit predictable patterns, rely on static signatures, and operate at human speeds. AI-driven cyberattacks systematically exploit the architectural flaws inherent in these legacy controls.
| Security Layer | Legacy Defensive Mechanism | Architectural Flaw Exposed by AI |
| Antivirus (AV) | File hashing (SHA-256) & static signature databases | Polymorphic engines rewrite code on every execution |
| Secure Email Gateway (SEG) | Keyword matching, domain age, and sender reputation scoring | LLMs generate zero-defect, highly contextualized copy |
| Push/SMS Multi-Factor Authentication | Out-of-band numeric codes and simple approval prompts | Adversaries execute automated push fatigue & SIM-swapping |
Signature-Based Antivirus Deficits
Traditional antivirus software relies on known indicator-of-compromise (IoC) databases. When an AI engine generates a novel, polymorphic binary for a single target, the file’s cryptographic hash (e.g., SHA-256) has never been cataloged by threat intelligence feeds. The legacy endpoint security tool allows the execution because no signature match exists.
Secure Email Gateway (SEG) Limitations
Traditional email security platforms filter incoming messages using bad-word lists, known malicious URL links, and domain age reputation metrics. AI-generated phishing messages contain no spam keywords, utilize clean phrasing, and frequently use compromised, high-reputation OAuth tokens or compromised legitimate accounts to transmit messages. Consequently, SEGs mark the email as benign and deliver it directly to the user’s inbox.
Push-Notification & SMS 2FA Inefficiencies
Legacy multi-factor authentication (MFA) that relies on SMS text messages or basic “Approve/Deny” mobile prompts fails against automated adversary-in-the-middle (AiTM) proxy toolkits. Frameworks like Evilginx intercept session tokens in real time. Furthermore, automated AI scripts execute ‘MFA fatigue’ spams—sending hundreds of verification prompts late at night until an employee accidentally approves access. To systematically harden your identity perimeter against these credential attacks, follow our step-by-step Multi-Factor Authentication Setup Guide for SMBs (2026).
AI-Driven Cyberattacks: How to Defend (Actionable Blueprint)
To successfully defend against machine-speed intrusions, enterprise security postures must transition from reactive perimeter defense to an adaptive, zero-trust framework centered on behavioral telemetry and hardware-enforced identity controls. Review the official CISA AI Cybersecurity Guidance for federal standards on securing automated environments.
Step 1: Deploying Behavioral Endpoint Detection & Response (EDR/XDR)
Replace legacy antivirus solutions with behavioral EDR/XDR platforms such as CrowdStrike Falcon, SentinelOne Singularity, or Microsoft Defender XDR. Rather than evaluating static file attributes, these tools monitor real-time process behavior, memory allocation calls, and parent-child process relationships.
Security teams must configure strict rule sets to detect administrative tools being used maliciously (Living off the Land). For example, auditing process mitigations on System32 processes like lsass.exe and enabling Defender’s Attack Surface Reduction (ASR) Rule 9e6c4e0a-74d9-476e-b326-119c373b7073 directly blocks credential stealing attempts from system memory. For a broader framework on keeping underlying host infrastructures tuned and secure against automated scanning, review our Server Performance Management: Proven 2026 Guide.
Detecting abnormal system calls—such as rundll32.exe calling comsvcs.dll to dump process memory—allows behavioral EDR engines to terminate the process instantly, stopping credential theft before privilege escalation occurs. Implementing real-time behavioral analytics remains one of the primary tactics when evaluating AI-driven cyberattacks and how to defend critical endpoints.
Step 2: Transitioning to FIDO2 / Hardware-based Phishing-Resistant MFA
Migrate your enterprise identity architecture from SMS and push notifications to FIDO2/WebAuthn hardware security keys (such as YubiKeys) or platform passkeys. FIDO2 binds the authentication credential directly to the specific domain origin (e.g., login.microsoftonline.com). Even if an AI-driven AiTM proxy trick an employee into entering credentials on a spoofed domain, the hardware key refuses to pass the assertion signature to the unauthenticated site, completely mitigating credential interception. To baseline these standards against official federal benchmarks, consult the NIST Multi-Factor Authentication Guidelines.
Step 3: Out-of-Band Financial & Administrative Protocols
Operational policies must be updated to address deepfake audio and video cloning. Mandate strict out-of-band (OOB) authorization procedures for any sensitive action:
- Financial Approvals: Wire transfers exceeding a set threshold (e.g., $5,000) require secondary verification using a known, offline contact number—never the contact details provided in the incoming request email or call.
- Administrative Operations: Privilege escalation requests, API key generation, or global tenant settings alterations require dual-custody approval within your Identity and Access Management (IAM) platform.
- Shared Passphrases: Establish offline, pre-shared verbal passphrases for C-suite executives and administrative assistants to verify identity during emergency requests.
Step 4: Least Privilege Enforcement for Internal AI Agents & Service Accounts
Autonomous AI tools, internal LLM copilot plugins, and service accounts represent major enterprise attack vectors. Audit all non-human identities regularly:
- Enforce the Principle of Least Privilege (PoLP): Ensure service accounts possess only the exact read/write permissions required for their specific role.
- Terminate dormant OAuth grants and third-party SaaS integrations that request broad read-write access to corporate repositories or email databases.
- Implement automated key rotation schedules (maximum 30-day life cycles) for API access tokens used by internal AI scripts.
Step 5: Live Deepfake Simulation & Team Readiness Exercises
Traditional annual awareness training fails to prepare employees for modern threat tactics. Security teams should conduct quarterly live-fire exercise simulations:
- Run simulated phishing exercises using LLM-crafted contextual copy to train staff on identifying subtle contextual anomalies.
- Conduct authorized “vishing” simulations using cloned executive voices to test if financial controllers strictly adhere to out-of-band verification procedures.
- Establish clear, zero-penalty reporting mechanisms (e.g., a single-click “Report Phish” button in Outlook) to encourage early escalation of suspicious activity.
Technical Defense Comparison Matrix
| Threat Vector | Traditional Attack Profile | Modern AI-Driven Variant | Technical Defense Strategy | Deployment Complexity |
| Social Engineering & Phishing | Generic email blasts with obvious grammatical errors | Hyper-personalized, error-free copy generated by LLMs | FIDO2/WebAuthn Hardware Keys & NLP Email Analysis | Medium (Hardware token distribution required) |
| Executive BEC Fraud | Spoofed email headers or lookalike domain names | Real-time generative voice & video deepfake cloning | Out-of-Band verification protocols & shared verbal passphrases | Low (Policy enforcement & process updates) |
| Endpoint Compromise | Static executable files caught by hash signatures | Polymorphic binaries that alter code dynamically | Behavioral EDR/XDR telemetry with strict process rules | Medium (Agent rollout & policy tuning) |
| Credential Theft | Manual password dumping via standard tools (Mimikatz) | Automated LSASS memory scraping & token theft | Credential Guard, ASR rules, & Zero-Trust IAM policies | High (Enterprise Active Directory / IAM rebuild) |
| Network Reconnaissance | Manual port scanning and periodic vulnerability checks | Autonomous bots probing edge systems continuously | Micro-segmentation & automated exposure management platforms | High (Network mapping & firewall redesign) |
Executive FAQs
How does a Zero-Trust Architecture mitigate AI-driven cyberattacks?
Zero Trust operates on the fundamental principle of “never trust, always verify.” Rather than relying on a hard outer perimeter, Zero Trust enforces micro-segmentation, continuous identity validation, and strict context-aware access policies across every device, user, and workload. Even if an AI attack vector successfully compromises an endpoint or credential, Zero Trust boundaries prevent the adversary from moving laterally across the enterprise network.
What immediate controls prevent financial loss from voice-cloning deepfakes?
Technological tools alone cannot block a voice-cloning attack occurring on a standard phone line. The most effective defense is a strict administrative policy requiring out-of-band (OOB) authentication. Mandate that any request to transfer funds, modify payment details, or reveal sensitive credentials must be confirmed via a secondary communication channel using a verified number from the central directory—never relying on incoming caller ID or numbers included in the request.
How should IT departments handle “Shadow AI” tools used by employees?
Employees frequently paste proprietary code or corporate data into unauthorized third-party generative AI tools, exposing the enterprise to data leakage risks. Security teams must implement Cloud Access Security Broker (CASB) policies and Secure Web Gateways (SWG) to block access to unapproved AI endpoints. Concurrently, organizations should provide an enterprise-sanctioned, secure LLM environment with strict data-privacy controls (preventing vendor model training on corporate inputs) to fulfill employee operational needs safely.
Immediate 5-Point Operational Checklist
When evaluating organizational posture against AI-driven cyberattacks, how to defend enterprise assets comes down to rapid execution of these five core controls:
- Audit MFA Deployment: Immediately revoke SMS and push-notification authentication methods across all core administrative accounts in favor of FIDO2 hardware keys.
- Upgrade Endpoint Protection: Confirm all production endpoints run a modern EDR/XDR agent set to “Block” mode for behavioral anomalies and LSASS process dumping.
- Enforce Out-of-Band Policies: Publish an explicit corporate wire-transfer and credential-reset policy mandating offline secondary channel verification.
- Prune SaaS & Service Permissions: Revoke unused API keys, OAuth tokens, and excessive read/write permissions assigned to third-party integrations and non-human identities.
- Schedule Live-Fire Drills: Replace annual compliance slide decks with realistic AI-driven phishing and voice-cloning simulations to evaluate your organization’s actual operational readiness.